


Microsoft Security Operations Analyst - SC-200 Exam Questions
QUESTION NO: 1
You have a Microsoft 365 subscription that contains the following resources:
* 100 users that are assigned a Microsoft 365 E5 license
* 100 Windows 11 devices that are joined to the Microsoft Entra tenant
The users access their Microsoft Exchange Online mailbox by using Outlook on the web.
You need to ensure that if a user account is compromised, the Outlook on the web session token can be revoked.
What should you configure?
Correct Answer: C
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 2
You have an Azure subscription.
You plan to implement an Microsoft Sentinel workspace. You anticipate that you will ingest 20 GB of security log data per day.
You need to configure storage for the workspace. The solution must meet the following requirements:
* Minimize costs for daily ingested data.
* Maximize the data retention period without incurring extra costs.
What should you do for each requirement? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.
Correct Answer:

Explanation:
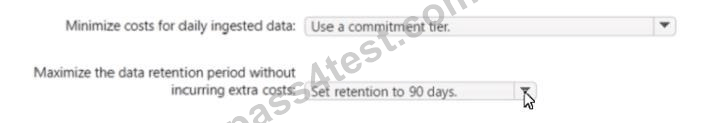
When designing a Microsoft Sentinel workspace, cost optimization and data retention management are two key considerations. Microsoft Sentinel stores data in an Azure Log Analytics workspace, and pricing for data ingestion and retention is managed through Log Analytics settings.
Minimize costs for daily ingested data:Microsoft's documentation on Log Analytics pricing models states that you can choose between Pay-As-You-Go (PAYG) and Commitment Tiers. The Commitment Tier model allows you to commit to a fixed amount of daily ingestion (for example, 20 GB/day in this case) at a lower per-GB cost compared to PAYG pricing. If your ingestion volume is predictable (as in this scenario-20 GB per day), this model provides significant cost savings without the administrative overhead of managing caps or throttling.Therefore, to minimize ingestion cost, the correct choice is "Use a commitment tier." Maximize the data retention period without incurring extra costs:By default, Microsoft Sentinel (via Log Analytics) provides 90 days of data retention at no additional charge. Extending retention beyond 90 days incurs additional storage charges. According to Microsoft's official guidance, "Log Analytics retains data for
90 days at no cost; data kept beyond that period is billed at the retention rate."Therefore, to maximize the free retention period while avoiding extra cost, the correct configuration is "Set retention to 90 days." Summary:
Minimize costs for daily ingested data # Use a commitment tier
Maximize retention without extra costs # Set retention to 90 days
This configuration ensures both cost efficiency and maximum free data availability, aligning with Microsoft Security Operations (SecOps) and Sentinel best practices.
QUESTION NO: 3
You have an Azure subscription.
You need to delegate permissions to meet the following requirements:
Enable and disable Azure Defender.
Apply security recommendations to resource.
The solution must use the principle of least privilege.
Which Azure Security Center role should you use for each requirement? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:

In Azure Security Center (now Microsoft Defender for Cloud), different roles have different levels of permission. To meet the principle of least privilege, you must assign only the minimal role required for each action.
Enable and disable Azure Defender
Enabling or disabling Microsoft Defender plans (formerly Azure Defender) changes billing and protection settings at the subscription level.
According to Microsoft documentation:
"Only users with the Subscription Owner or Security Admin roles at the subscription level can enable or disable Microsoft Defender plans." Because this change affects billing and overall subscription configuration, the Subscription Owner role is the appropriate one - it has full control at the subscription scope.
Apply security recommendations to a resource
Applying recommendations (such as enabling disk encryption or updating system patches) involves managing configuration settings on specific resources.
The Resource Group Owner role provides full management access to all resources within that resource group, which includes the ability to implement or remediate recommendations.
Microsoft Defender for Cloud guidance states:
"To apply recommendations or perform remediation tasks on specific resources, the user must have write permissions on those resources - typically provided by the Resource Group Owner or Contributor role."
# Final Correct Mapping:
Enable and disable Azure Defender # Subscription Owner
Apply security recommendations to a resource # Resource Group Owner
QUESTION NO: 4
You have a Microsoft 365 E5 subscription that contains 100 Linux devices. The devices are onboarded to Microsoft Defender 365. You need to initiate the collection of investigation packages from the devices by using the Microsoft 365 Defender portal. Which response action should you use?
You have a Microsoft 365 E5 subscription that contains 100 Linux devices. The devices are onboarded to Microsoft Defender 365. You need to initiate the collection of investigation packages from the devices by using the Microsoft 365 Defender portal. Which response action should you use?
Correct Answer: D
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 5
You have the resources shown in the following table.

You need to prevent duplicate events from occurring in SW1.
What should you use for each action? To answer, drag the appropriate resources to the correct actions. Each resource may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

You have the resources shown in the following table.
You need to prevent duplicate events from occurring in SW1.
What should you use for each action? To answer, drag the appropriate resources to the correct actions. Each resource may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
| From the Syslog configuration, remove the facilities that send CEF messages. | CEF1 | | From the Log Analytics agent, disable Syslog synchronization. | Server2 | The goal is to eliminate duplicate events in the Azure Sentinel workspace (SW1). Duplication typically occurs when the same log source is sending data to Azure Sentinel via multiple collection methods.
Analysis of the Environment
SW1 is the Azure Sentinel (now Microsoft Sentinel) workspace, which is the final destination for all logs.
CEF1 is a Linux server configured as a log forwarder (often called a CEF collector) for Microsoft Sentinel. It uses the Log Analytics agent (or the newer Azure Monitor Agent) to ingest logs and is specifically configured to forward Common Event Format (CEF) logs to SW1.
Server1 sends CEF logs to CEF1. This is the intended, single collection path for Server1 ' s CEF logs: Server1 CEF1 SW1. No duplication is inherent here.
Server2 sends Syslog logs to CEF1. This path is: Server2 CEF1 SW1.
Since CEF1 is running the Log Analytics agent (required to forward logs to SW1) and is configured to collect Syslog data (to receive Server2 ' s logs), the Log Analytics agent on CEF1 will also attempt to ingest the Syslog messages it receives into SW1.
However, the Log Analytics agent itself can also be used to collect Syslog/CEF logs directly from the source server.
Addressing Duplication
Duplication is most likely to occur if a server is sending the same logs to a forwarder AND also has the Log Analytics agent configured to send the same logs directly to SW1.
Action 1: From the Syslog configuration, remove the facilities that send CEF messages.
Resource: CEF1
Reasoning: CEF1 is a Linux server running the Log Analytics agent and is acting as the collector. Server1 sends CEF logs to CEF1. These CEF logs are transmitted using Syslog (specifically, a custom Syslog format).
If the Log Analytics agent on CEF1 is configured to collect all Syslog facilities, it will ingest the raw CEF Syslog messages it receives from Server1 AND also ingest the parsed CEF messages via its custom forwarding logic. To prevent the Syslog collector on CEF1 from ingesting the raw CEF messages that it is supposed to be forwarding, you must modify its Syslog configuration (e.g., in /etc/rsyslog.conf or equivalent) to ignore the facilities/log files used by the incoming CEF messages from Server1. The primary purpose of CEF1 is to receive and forward CEF, not to have its Log Analytics agent ingest the raw Syslog that transports the CEF payload.
Action 2: From the Log Analytics agent, disable Syslog synchronization.
Resource: Server2
Reasoning: Server2 is configured to send Syslog logs to CEF1 (Server2 CEF1 SW1). Since Server2 is a Linux server, it may also have the Log Analytics agent installed for other monitoring purposes. If the Log Analytics agent on Server2 is installed, it is configured by default to collect Syslog logs directly and send them to SW1 (Server2 SW1). This creates a duplicate path for the Syslog data:
Path A (Intended): Server2 Syslog CEF1 SW1
Path B (Duplication): Server2 Log Analytics Agent Syslog SW1
According to Microsoft Sentinel documentation on log ingestion, when using a dedicated forwarder (like CEF1) for Syslog/CEF, you must disable the Syslog collection on the Log Analytics agent of the source machine (Server2) to prevent this duplication. This is typically done by disabling Syslog synchronization in the Log Analytics agent configuration or removing the Syslog entry from the agent ' s data sources.
References: Microsoft Sentinel documentation on data connectors for Syslog and CEF, specifically the sections discussing the deployment of the Log Analytics agent and forwarders, which repeatedly warn about the need to prevent dual-ingestion of the same log type (Syslog or CEF) from both the source server ' s agent and a dedicated collector/forwarder.
QUESTION NO: 6
You have an Azure subscription that uses Microsoft Defender for Servers Plan 1 and contains a server named Server1.
You enable agentless scanning.
You need to prevent Server1 from being scanned. The solution must minimize administrative effort.
What should you do?
You have an Azure subscription that uses Microsoft Defender for Servers Plan 1 and contains a server named Server1.
You enable agentless scanning.
You need to prevent Server1 from being scanned. The solution must minimize administrative effort.
What should you do?
Correct Answer: B
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 7
You have a Microsoft 365 E5 subscription that uses Microsoft Copilot for Security. You plan to run the following code to create a custom Copilot for Security plugin.

You need to specify a format and complete the code segment. Which format should you use for the < target > variable?
You have a Microsoft 365 E5 subscription that uses Microsoft Copilot for Security. You plan to run the following code to create a custom Copilot for Security plugin.
You need to specify a format and complete the code segment. Which format should you use for the < target > variable?
Correct Answer: A
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 8
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint You need to create a query that will link the Alertlnfo, AlertEvidence, and DeviceLogonEvents tables. The solution must return all the rows in the tables.
Which operator should you use?
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint You need to create a query that will link the Alertlnfo, AlertEvidence, and DeviceLogonEvents tables. The solution must return all the rows in the tables.
Which operator should you use?
Correct Answer: D
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 9
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: You add the accounts to an Active Directory group and add the group as a Sensitive group.
Does this meet the goal?
Correct Answer: B
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 10
You have a Microsoft 365 subscription that uses Microsoft Defender for Office 365.
You have Microsoft SharePoint Online sites that contain sensitive documents. The documents contain customer account numbers that each consists of 32 alphanumeric characters.
You need to create a data loss prevention (DLP) policy to protect the sensitive documents. What should you use to detect which documents are sensitive?
Correct Answer: D
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 11
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.
Correct Answer:

Explanation:

Reference:
For CEF ingestion, Microsoft Sentinel uses a Linux "log forwarder" that runs the Log Analytics agent (OMS agent) and a syslog daemon (rsyslog/syslog-ng). The documented deployment flow is: first install the Log Analytics agent on the forwarder and connect it to your Sentinel workspace (Workspace ID/Key). Next, configure the agent to listen on TCP/UDP port 25226-the port the OMS agent uses to receive CEF-translated syslog messages locally-and forward them to the connected workspace (this forwarding is inherent once the agent is connected). Then configure the syslog daemon to receive the external product's CEF events on the chosen syslog port (commonly 514) and forward them locally to 127.0.0.1:25226. Finally, restart rsyslog
/syslog-ng and the OMS agent to apply changes. You do not forward events "directly to Sentinel" from syslog; the agent handles transport to the workspace. An OMS Gateway is only required when the forwarder has no direct Internet access and isn't part of the standard, minimal-effort path. This sequence ensures reliable, supported ingestion of CEF messages into Microsoft Sentinel with the least administrative overhead.
QUESTION NO: 12
You have a Microsoft Sentinel workspace.
You need to create a KQL query that will identify successful sign-ins from multiple countries during the last three hours.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point
Correct Answer:

Explanation:

Below is the completed KQL that meets the requirement (successful sign-ins from multiple countries in the last 3 hours), using the ASIM authentication schema commonly used in Microsoft Sentinel:
let timeframe = ago(3h);
let threshold = 5;
imAuthentication
| where TimeGenerated > timeframe
| where EventType == " Logon " and EventResult == " Success "
| where isnotempty(SrcGeoCountry)
| summarize
StartTime = min(TimeGenerated),
EndTime = max(TimeGenerated),
Vendors = make_set(EventVendor),
Products = make_set(EventProduct),
NumOfCountries = dcount(SrcGeoCountry)
by TargetUserId, TargetUserPrincipalName, TargetUserType
| where NumOfCountries > threshold
Blade/source: imAuthentication (ASIM parser) normalizes authentication data across sources in Sentinel, letting you query sign-ins consistently.
Filters: EventType == " Logon " and EventResult == " Success " restrict to successful logons.
Geo dimension: SrcGeoCountry is the normalized source country field for the sign-in.
Logic: We look back 3 hours, count distinct countries per user with dcount(SrcGeoCountry), and keep only users exceeding a chosen threshold (e.g., > 5).
This delivers exactly "successful sign-ins from multiple countries during the last three hours," ready for use in a hunting query or to form a scheduled analytics rule.
QUESTION NO: 13
You have on-premises servers that run Windows Server.
You have a Microsoft Sentinel workspace named SW1. SW1 is configured to collect Windows Security log entries from the servers by using the Azure Monitor Agent data connector.
You plan to limit the scope of collected events to events 4624 and 462S only.
You need to use a PowerShell script to validate the syntax of the filter applied to the connector.
How should you complete the script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:

According to Microsoft Sentinel and Azure Monitor Agent (AMA) documentation, when configuring data collection from Windows Security logs, you can use XPath filtering to limit which event IDs are collected.
This helps optimize data ingestion by filtering out unnecessary events.
In this scenario, the requirement is to collect only event IDs 4624 (successful sign-in) and 4625 (failed sign- in). The PowerShell cmdlet Get-WinEvent supports several filtering methods: -FilterXPath, -FilterHashtable, and -FilterXml. To test the same XPath syntax used by the connector, you must use -FilterXPath, because this option accepts the same XPath query string format as used in the AMA data collection rule (DCR).
The correct XPath syntax for filtering specific event IDs from the Security log is:
Security!*[System[(EventID=4624 or EventID=4625)]]
This expression instructs the event query to return only events from the Security log whose EventID equals
4624 or 4625.
Finally, to validate the filter, you run:
Get-WinEvent -LogName ' Security ' -FilterXPath $events
This command executes the filter locally and confirms that the syntax correctly retrieves the intended events.
Therefore, the correct completed script is:
# $events = ' Security!*[System[(EventID=4624 or EventID=4625)]] '
# Get-WinEvent -LogName ' Security ' -FilterXPath $events
QUESTION NO: 14
You have a custom analytics rule to detect threats in Azure Sentinel.
You discover that the analytics rule stopped running. The rule was disabled, and the rule name has a prefix of AUTO DISABLED.
What is a possible cause of the issue?
You have a custom analytics rule to detect threats in Azure Sentinel.
You discover that the analytics rule stopped running. The rule was disabled, and the rule name has a prefix of AUTO DISABLED.
What is a possible cause of the issue?
Correct Answer: A
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 15
You need to implement the scheduled rule for incident generation based on rulequery1.
What should you configure first?
You need to implement the scheduled rule for incident generation based on rulequery1.
What should you configure first?
Correct Answer: C
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).

