


GIAC Critical Controls Certification (GCCC) - GCCC Exam Questions
QUESTION NO: 1
An organization has created a policy that allows software from an approved list of applications to be installed on workstations. Programs not on the list should not be installed. How can the organization best monitor compliance with the policy?
An organization has created a policy that allows software from an approved list of applications to be installed on workstations. Programs not on the list should not be installed. How can the organization best monitor compliance with the policy?
Correct Answer: B
QUESTION NO: 2
John a network administrator at Northeast High School. Faculty have been complaining that although they can detect and authenticate to the faculty wireless network, they are unable to connect. While troubleshooting, John discovers that the wireless network server is out of DHCP addresses due to a large number of unauthorized student devices connecting to the network. Which course of action would be an effective temporary stopgap to secure the network until a permanent solution can be found?
John a network administrator at Northeast High School. Faculty have been complaining that although they can detect and authenticate to the faculty wireless network, they are unable to connect. While troubleshooting, John discovers that the wireless network server is out of DHCP addresses due to a large number of unauthorized student devices connecting to the network. Which course of action would be an effective temporary stopgap to secure the network until a permanent solution can be found?
Correct Answer: A
QUESTION NO: 3
Which projects enumerates or maps security issues to CVE?
Which projects enumerates or maps security issues to CVE?
Correct Answer: D
QUESTION NO: 4
What type of Unified Modelling Language (UML) diagram is used to show dependencies between logical groupings in a system?
What type of Unified Modelling Language (UML) diagram is used to show dependencies between logical groupings in a system?
Correct Answer: D
QUESTION NO: 5
Which of the following is used to prevent spoofing of e-mail addresses?
Which of the following is used to prevent spoofing of e-mail addresses?
Correct Answer: C
QUESTION NO: 6
Which of the following actions will assist an organization specifically with implementing web application software security?
Which of the following actions will assist an organization specifically with implementing web application software security?
Correct Answer: D
QUESTION NO: 7
Dragonfly Industries requires firewall rules to go through a change management system before they are configured. Review the change management log. Which of the following lines in your firewall ruleset has expired and should be removed from the configuration?
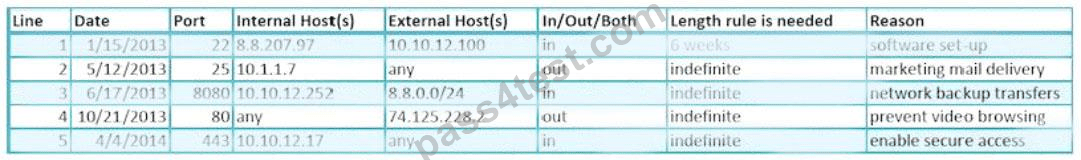
Dragonfly Industries requires firewall rules to go through a change management system before they are configured. Review the change management log. Which of the following lines in your firewall ruleset has expired and should be removed from the configuration?
Correct Answer: A
QUESTION NO: 8
What could a security team use the command line tool Nmap for when implementing the Inventory and Control of Hardware Assets Control?
What could a security team use the command line tool Nmap for when implementing the Inventory and Control of Hardware Assets Control?
Correct Answer: B
QUESTION NO: 9
An auditor is focusing on potential vulnerabilities. Which of the following should cause an alert?
An auditor is focusing on potential vulnerabilities. Which of the following should cause an alert?
Correct Answer: B
QUESTION NO: 10
An organization has implemented a policy to detect and remove malicious software from its network. Which of the following actions is focused on correcting rather than preventing attack?
An organization has implemented a policy to detect and remove malicious software from its network. Which of the following actions is focused on correcting rather than preventing attack?
Correct Answer: D

