


Microsoft Administering Windows Server - AZ-802 Exam Questions
QUESTION NO: 1
Your on-premises datacenter contains physical servers and Hyper-V virtual machines.
You have an Azure subscription.
You plan to use Azure Migrate to perform the following tasks:
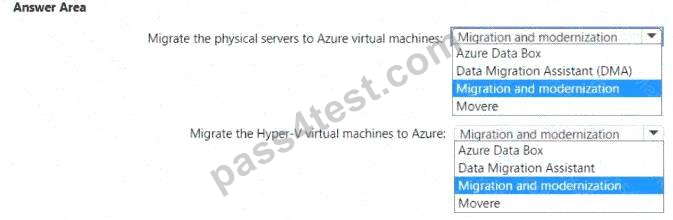
* Migrate the physical servers to Azure virtual machines.
* Migrate the Hyper-V virtual machines to Azure.
What should you use for each task? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Your on-premises datacenter contains physical servers and Hyper-V virtual machines.
You have an Azure subscription.
You plan to use Azure Migrate to perform the following tasks:
* Migrate the physical servers to Azure virtual machines.
* Migrate the Hyper-V virtual machines to Azure.
What should you use for each task? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Correct Answer:
Explanation:
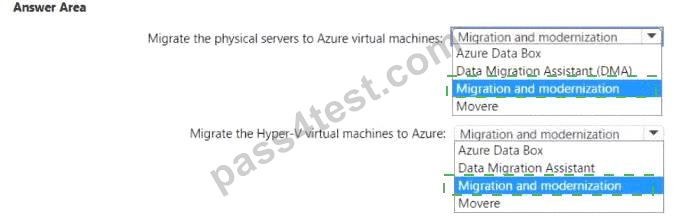
Migrate the physical servers to Azure virtual machines: Migration and modernization. Migrate the Hyper-V virtual machines to Azure: Migration and modernization.
Inside the Azure Migrate hub, the Migration and modernization tool, also known as Azure Migrate: Server Migration, is the single unified tool that handles both agent-based replication of physical servers, as well as virtual machines from other clouds, and agentless replication of on-premises Hyper-V virtual machines directly into Azure virtual machines. Because both tasks in this scenario, migrating physical servers and migrating Hyper-V VMs, fall within the scope of this same tool, Migration and modernization is the correct choice for each answer position. Azure Data Box is used for large-scale offline bulk data transfers rather than for live server or VM migration, Data Migration Assistant is scoped specifically to assessing and migrating SQL Server databases, and Movere is a discovery and inventory tool used to assess an environment before migration rather than an engine that performs the actual migration. None of those three tools perform the server or VM migration itself, so Migration and modernization is the only option among those listed that correctly answers both parts of this question.
QUESTION NO: 2
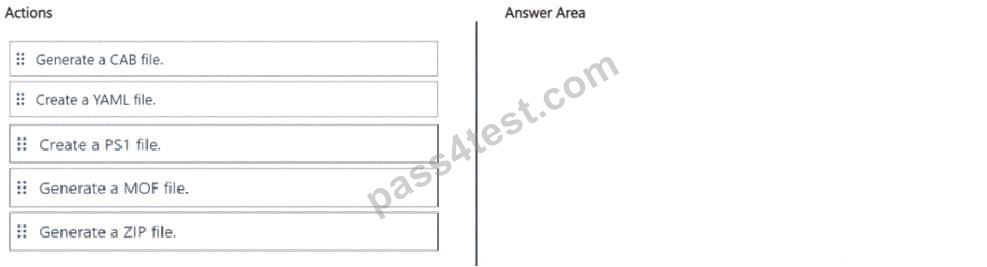
You have an Azure subscription. The subscription contains multiple virtual machines that run Windows Server. You need to create an Azure Machine Configuration package. Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
You have an Azure subscription. The subscription contains multiple virtual machines that run Windows Server. You need to create an Azure Machine Configuration package. Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Correct Answer:
Explanation:
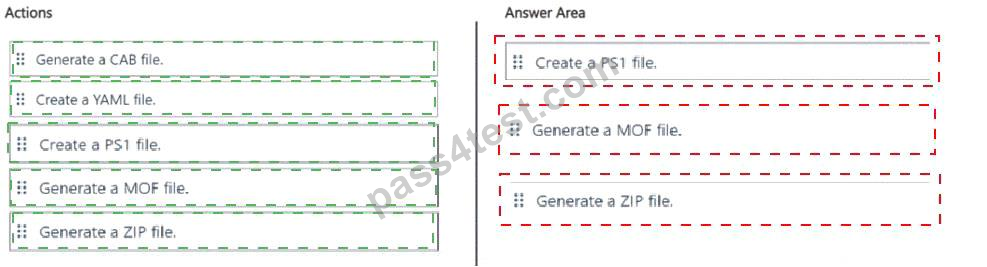
1. Create a PS1 file. 2. Generate a MOF file. 3. Generate a ZIP file.
Building an Azure Machine Configuration (Guest Configuration) package begins with authoring the desired- state logic as a PowerShell Desired State Configuration script, saved as a .ps1 file that defines a DSC configuration block describing the settings to audit or enforce. That DSC configuration must then be compiled
-- by invoking (running) the configuration function defined in the .ps1 file -- which produces a Managed Object Format (.mof) file, the actual, compiled desired-state document that the DSC/Guest Configuration engine consumes at runtime. Finally, the compiled MOF (together with any required supporting resource modules) is packaged using the GuestConfiguration PowerShell module ' s package-creation cmdlet (New- GuestConfigurationPackage), which produces the distributable package as a ZIP file -- this ZIP is the artifact actually referenced by an Azure Policy guest configuration definition and deployed/audited against target machines. Generating a CAB file and creating a YAML file are both unrelated to this workflow: CAB files are used for driver/update packaging, and YAML files are typically associated with Azure DevOps pipeline definitions or Bicep/ARM-adjacent tooling, neither of which is part of building a Machine Configuration package. Therefore, the correct sequence is: create a PS1 file, generate a MOF file, and generate a ZIP file.
QUESTION NO: 3
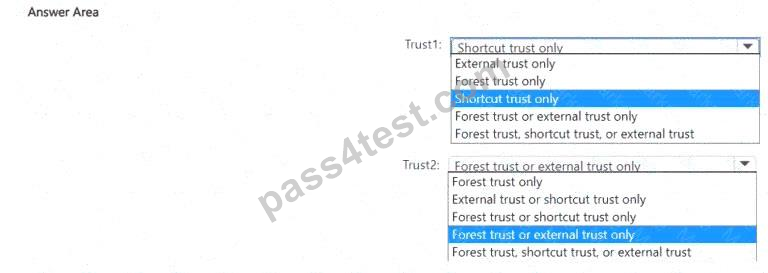
Your network contains the domains shown in the following exhibit: a forest rooted at contoso.com, with a child domain west.contoso.com, and a grandchild domain sub.west.contoso.com; a separate, unrelated domain fabrikam.com. You need to establish trust relationships as shown in the following exhibit: Trust1, directly between contoso.com and sub.west.contoso.com (bypassing the intermediate west.contoso.com); Trust2, between contoso.com and fabrikam.com. Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
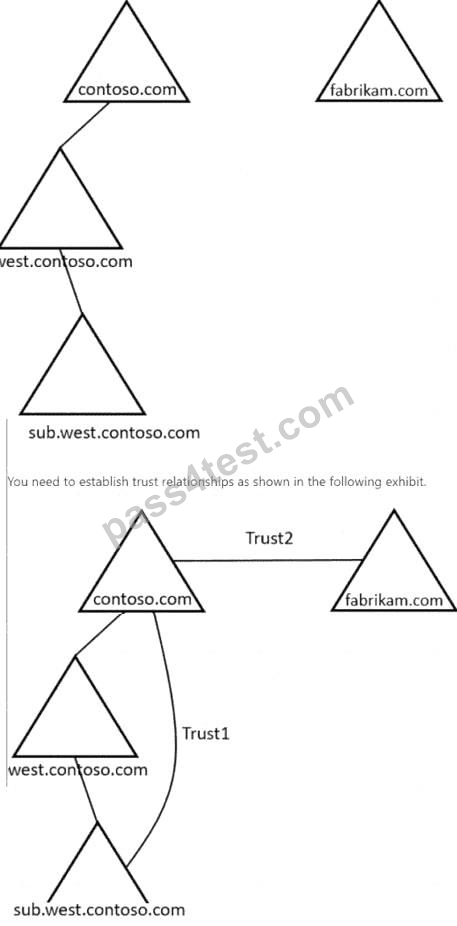
Domain tree and trust diagram
Your network contains the domains shown in the following exhibit: a forest rooted at contoso.com, with a child domain west.contoso.com, and a grandchild domain sub.west.contoso.com; a separate, unrelated domain fabrikam.com. You need to establish trust relationships as shown in the following exhibit: Trust1, directly between contoso.com and sub.west.contoso.com (bypassing the intermediate west.contoso.com); Trust2, between contoso.com and fabrikam.com. Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Domain tree and trust diagram
Correct Answer:
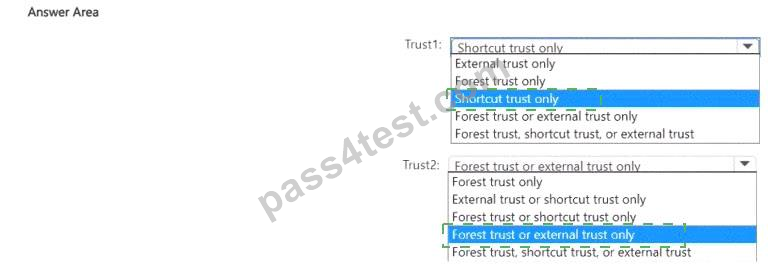
Explanation:
Trust1: Shortcut trust only. Trust2: Forest trust or external trust only.
Contoso.com, west.contoso.com, and sub.west.contoso.com are all part of the same single Active Directory forest, related in a parent-child-grandchild domain tree; within one forest, all domains already trust each other transitively through the automatically created parent-child trusts, but authentication referrals between two domains that are several hops apart in the tree (such as the forest root, contoso.com, and a grandchild domain, sub.west.contoso.com) must otherwise traverse every intermediate domain in the tree, which adds authentication latency. A shortcut trust is specifically designed to create a direct, transitive trust path between two domains in the same forest that are not directly adjacent in the domain hierarchy, cutting out the intermediate hops -- exactly matching Trust1 ' s requirement. A forest trust or external trust would not apply here, since those are used to connect separate forests or separate domains outside a shared forest, not two domains already inside the same forest. Fabrikam.com, by contrast, is an entirely separate domain/forest with no existing trust relationship to contoso.com, so a shortcut trust (which only works between domains in the same forest) is not an option for Trust2. Depending on whether fabrikam.com is a single-domain forest that should be fully, transitively trusted or only a single domain needing a narrower, non-transitive relationship, Trust2 can be established as either a forest trust (transitive, connecting the two entire forests) or an external trust (non-transitive, domain-to-domain only).
QUESTION NO: 4
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You have 50 Azure virtual machines that run Windows Server. You need to ensure that any security exploits detected on the virtual machines are forwarded to Defender for Cloud. Which extension should you enable on the virtual machines?
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You have 50 Azure virtual machines that run Windows Server. You need to ensure that any security exploits detected on the virtual machines are forwarded to Defender for Cloud. Which extension should you enable on the virtual machines?
Correct Answer: D
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 5
You have 50 on-premises servers that run Windows Server.
You have an Azure subscription that contains a Microsoft Sentinel workspace.
You plan to monitor the servers by using Microsoft Sentinel.
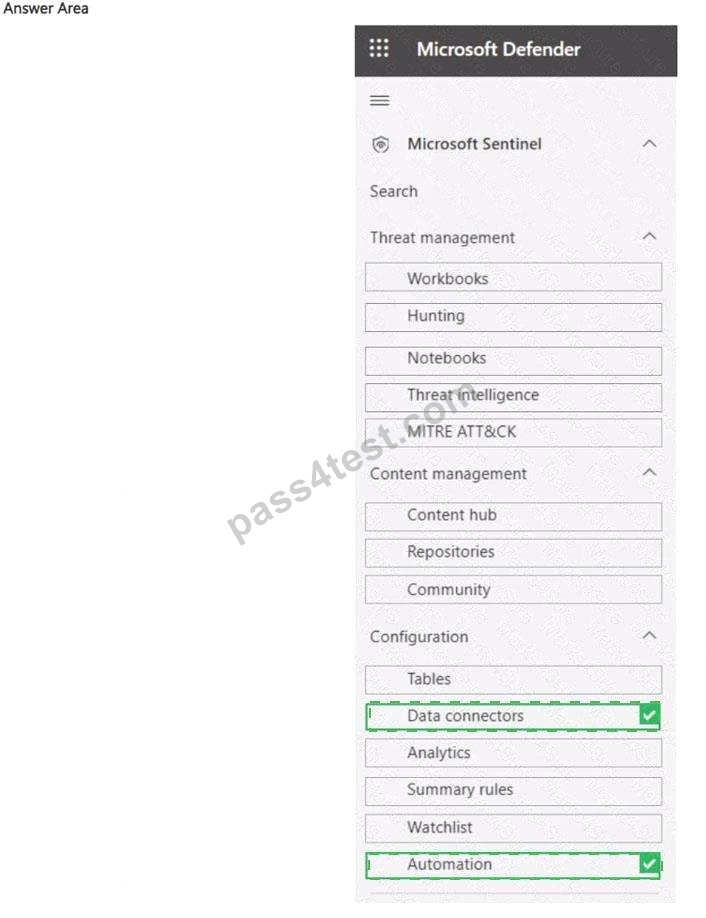
You need to perform the following actions in Microsoft Sentinel;
* Add the Windows Forwarded Events data connector.
* Create a playbook that has an incident trigger.
Which two settings should you use? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
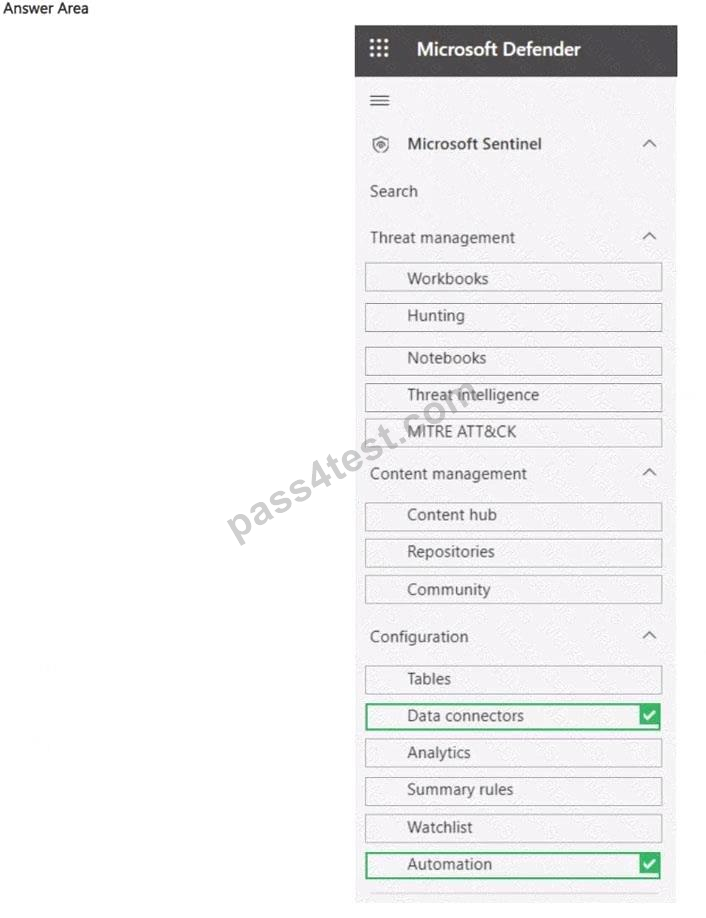
Exhibit
You have 50 on-premises servers that run Windows Server.
You have an Azure subscription that contains a Microsoft Sentinel workspace.
You plan to monitor the servers by using Microsoft Sentinel.
You need to perform the following actions in Microsoft Sentinel;
* Add the Windows Forwarded Events data connector.
* Create a playbook that has an incident trigger.
Which two settings should you use? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Exhibit
Correct Answer:
Explanation:
In the Microsoft Sentinel navigation pane, under the Configuration section, data connectors such as Windows Forwarded Events are added and configured from the Data connectors page, which is the purpose-built area of the workspace for enabling the underlying Log Analytics data connection that ingests forwarded Windows event log data from on-premises servers, typically by way of Azure Monitor Agent and Windows Event Forwarding. Automation rules and playbooks, including a Logic App-based playbook that starts with a Microsoft Sentinel incident trigger so it can run automated response steps whenever a new incident is created, are created and managed from the Automation page, which sits in the same Configuration section of the workspace navigation. These two pages are the specific, purpose-built areas of Microsoft Sentinel for connecting server-generated event data into the workspace and for building automated incident-response playbooks respectively, and they directly match the two actions described in the scenario: bringing in Windows Forwarded Events as a source, and wiring up an incident-triggered playbook to act on the alerts and incidents that source ultimately helps generate.
QUESTION NO: 6
Your network contains an Active Directory Domain Services (AD DS) domain.
The domain contains a file server named FS1 that hosts a file share named Finance. The domain contains an organizational unit (OU) named OU1 and a global security group named Group1.
A Group Policy Object (GPO) named GPO1 is linked to OU1.
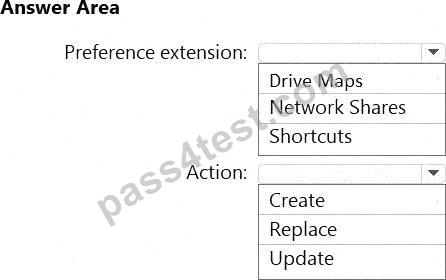
You need to configure a Group Policy Preferences item that maps drive F to \\FS1\Finance for the members of Group1.
The item will use Security Group item-level targeting and remove the preference setting when the setting no longer applies.
The solution must recreate the preference setting during Group Policy refresh if a user deletes or changes the setting.
What should you configure?
To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your network contains an Active Directory Domain Services (AD DS) domain.
The domain contains a file server named FS1 that hosts a file share named Finance. The domain contains an organizational unit (OU) named OU1 and a global security group named Group1.
A Group Policy Object (GPO) named GPO1 is linked to OU1.
You need to configure a Group Policy Preferences item that maps drive F to \\FS1\Finance for the members of Group1.
The item will use Security Group item-level targeting and remove the preference setting when the setting no longer applies.
The solution must recreate the preference setting during Group Policy refresh if a user deletes or changes the setting.
What should you configure?
To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:
Explanation:
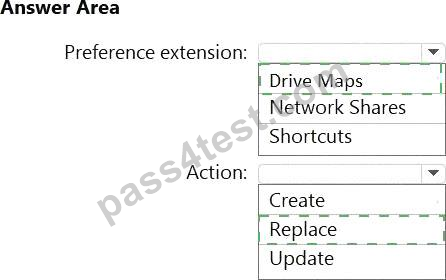
Preference extension: Drive Maps
Action: Replace
Group Policy Preferences provides the Drive Maps extension to create and manage mapped network drives for domain users.
The Drive Maps extension can assign drive F to the Finance share on FS1. Security Group item-level targeting ensures that the preference applies only to users who belong to Group1.
The Replace action deletes an existing mapped drive and recreates it during Group Policy refresh. This ensures that the configured mapping is restored even if a user modifies or removes it.
Selecting " Remove this item when it is no longer applied " also ensures that the mapping is removed when the user no longer meets the targeting conditions.
The Create action does not consistently recreate an existing modified mapping, while Update does not delete and rebuild the mapping.
Therefore, Drive Maps with Replace satisfies the requirements.
QUESTION NO: 7
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains two Hyper-V hosts named Server1 and Server2 that run Windows Server.
The Hyper-V hosts contain virtual machines that run Windows Server as shown in the following table:
VM1 - Virtual machine configuration version 10.0 - Server1
VM2 - Virtual machine configuration version 8.3 - Server1
VM3 - Virtual machine configuration version 9.3 - Server2
VM4 - Virtual machine configuration version 8.0 - Server2
You need to connect to the virtual machines by using PowerShell Direct.
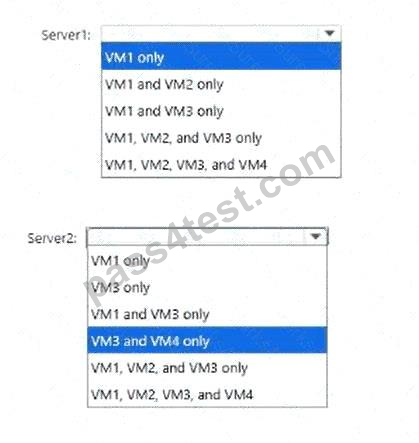
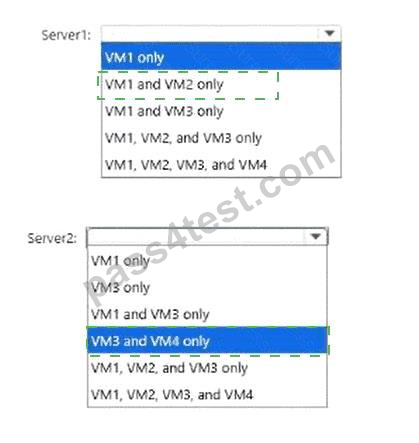
To which virtual machines can you connect from each Hyper-V host? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains two Hyper-V hosts named Server1 and Server2 that run Windows Server.
The Hyper-V hosts contain virtual machines that run Windows Server as shown in the following table:
VM1 - Virtual machine configuration version 10.0 - Server1
VM2 - Virtual machine configuration version 8.3 - Server1
VM3 - Virtual machine configuration version 9.3 - Server2
VM4 - Virtual machine configuration version 8.0 - Server2
You need to connect to the virtual machines by using PowerShell Direct.
To which virtual machines can you connect from each Hyper-V host? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:
Explanation:
Server1: VM1 and VM2
Server2: VM3 and VM4
PowerShell Direct lets an administrator run PowerShell inside a Windows VM directly from the Hyper-V host that owns that VM, without relying on network connectivity or WinRM configuration. Microsoft lists Windows Server 2016 or later for both host and guest and identifies virtual machine configuration version 6.2 as the minimum version supporting PowerShell Direct. Every VM in the table is above that minimum: VM1 is
10.0, VM2 is 8.3, VM3 is 9.3, and VM4 is 8.0. However, PowerShell Direct is local to the Hyper-V host; it is not a mechanism for connecting from one Hyper-V host to a VM running on another host. Therefore, Server1 can connect to VM1 and VM2, while Server2 can connect to VM3 and VM4.
QUESTION NO: 8
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the following servers:
Server1 has the DFS Namespaces role service installed.
Server2 has the DFS Namespaces role service installed.
Server3 hosts a file share named \\Server3\Share1.
Server4 hosts a file share named \\Server4\Share2.
You need to publish both file shares in a single DFS namespace named Corp. Corp must remain available if either Server1 or Server2 is unavailable.
What should you do?
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the following servers:
Server1 has the DFS Namespaces role service installed.
Server2 has the DFS Namespaces role service installed.
Server3 hosts a file share named \\Server3\Share1.
Server4 hosts a file share named \\Server4\Share2.
You need to publish both file shares in a single DFS namespace named Corp. Corp must remain available if either Server1 or Server2 is unavailable.
What should you do?
Correct Answer: B
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 9
You plan to deploy the Azure Monitor agent to 100 on-premises servers that run Windows Server. Which parameters should you provide when you install the agent?
You plan to deploy the Azure Monitor agent to 100 on-premises servers that run Windows Server. Which parameters should you provide when you install the agent?
Correct Answer: D
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).
QUESTION NO: 10
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a child domain named east.contoso.com and the servers shown in the following exhibit: DC1 (contoso.com, holds schema master/infrastructure master/domain naming master), DC2 (east.contoso.com, holds PDC emulator/RID master, is a global catalog server), Server1 (contoso.com, File Server/DFS Namespaces/DFS Replication roles - a member server, not a domain controller). You need to create a folder for the Central Store to manage Group Policy template files for the entire forest. What should you name the folder, and on which server should you create the folder? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
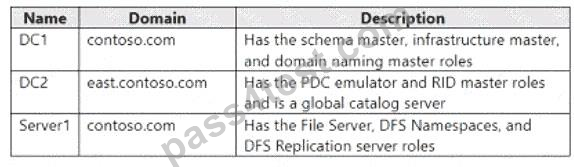
DC1 (contoso.com: schema/infra/domain-naming master) / DC2 (east.contoso.com: PDC+RID master, GC) / Server1 (contoso.com, member server: File Server/DFS Namespaces/DFSR).
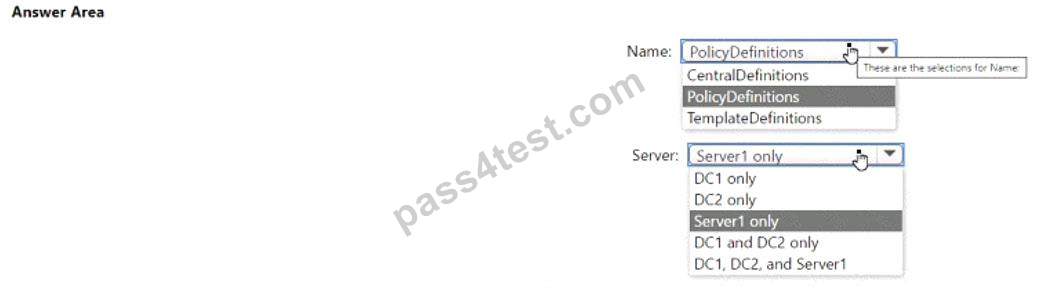
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a child domain named east.contoso.com and the servers shown in the following exhibit: DC1 (contoso.com, holds schema master/infrastructure master/domain naming master), DC2 (east.contoso.com, holds PDC emulator/RID master, is a global catalog server), Server1 (contoso.com, File Server/DFS Namespaces/DFS Replication roles - a member server, not a domain controller). You need to create a folder for the Central Store to manage Group Policy template files for the entire forest. What should you name the folder, and on which server should you create the folder? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
DC1 (contoso.com: schema/infra/domain-naming master) / DC2 (east.contoso.com: PDC+RID master, GC) / Server1 (contoso.com, member server: File Server/DFS Namespaces/DFSR).
Correct Answer:
Explanation:
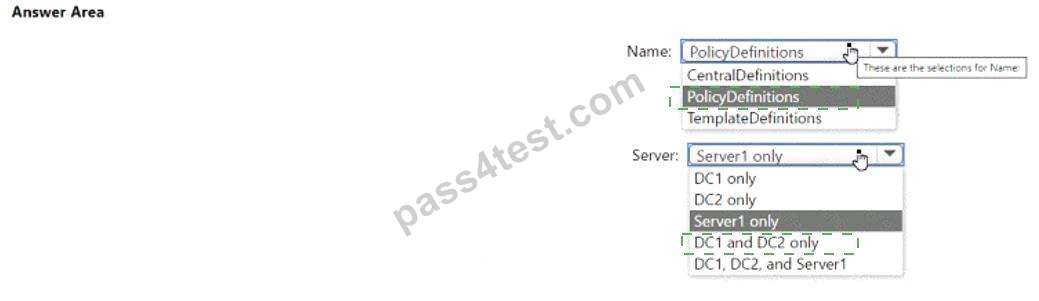
< Name: PolicyDefinitions ; Server: DC1 and DC2 only
The Group Policy Central Store is a specifically named folder, PolicyDefinitions, that must be created inside the SYSVOL share of a domain, at the path \\ < domain > \SYSVOL\ < domain > \Policies\PolicyDefinitions; Microsoft ' s Group Policy tooling looks for that exact folder name and will not recognize a differently named folder such as CentralDefinitions or TemplateDefinitions as a Central Store. Because SYSVOL only exists on domain controllers (it is replicated between DCs of a domain via DFS Replication), the folder can only be created on a machine that is a domain controller; Server1 is a plain member server hosting the File Server, DFS Namespaces, and DFS Replication roles, and has no SYSVOL share at all, so it cannot host the Central Store regardless of what other roles it runs. Critically, the Central Store is a per-domain construct: creating it inside contoso.com ' s SYSVOL (which DC1 hosts and which replicates to every DC in that domain) only benefits GPO editing sessions connected to contoso.com, and it has no effect on GPO editing in the separate child domain, east.contoso.com. To have Central Store coverage across the entire forest - meaning correctly working ADMX template resolution when administrators edit GPOs in either domain - a PolicyDefinitions folder must be created in the SYSVOL of both contoso.com (via DC1) and east.contoso.com (via DC2), which is why DC1 and DC2 together, not Server1 and not either domain controller alone, is the correct answer.
QUESTION NO: 11
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a DNS server named Server1. Server1 hosts a DNS zone named fabrikam.com that was signed by DNSSEC. You need to ensure that all the member servers in the domain perform DNSSEC validation for the fabrikam.com namespace. What should you do?
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a DNS server named Server1. Server1 hosts a DNS zone named fabrikam.com that was signed by DNSSEC. You need to ensure that all the member servers in the domain perform DNSSEC validation for the fabrikam.com namespace. What should you do?
Correct Answer: B
Explanation: Only visible for Pass4Test members. You can sign-up / login (it's free).

